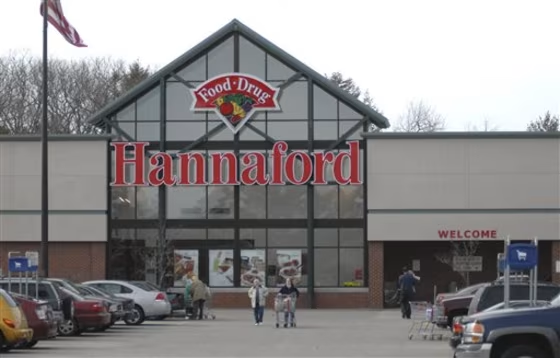
Unauthorized software that was secretly installed on servers in nearly all of Hannaford Bros. Co.'s supermarkets enabled the massive data breach that compromised up to 4.2 million credit and debit cards, the company said Friday.
The Scarborough, Maine-based grocer confirmed a report in The Boston Globe that it told Massachusetts regulators this week about the link to the illicit computer "malware."
The company doesn't know how the malware — short for malicious software — got to the stores' servers, Hannaford spokeswoman Carol Eleazer said.
"Virtually everything is possible," she said. "There are still many, many aspects that we don't totally understand."
The company has said that the data theft, which occurred between Dec. 7 and March 10, took place as shoppers swiped their cards at checkout line machines and the information was transmitted to banks for approval.
The malware turned up in all Hannaford stores in New England and New York, and in most of the company's affiliated Sweetbay stores in Florida, Eleazer said.
The finding was revealed in a letter from Hannaford general counsel Emily Dickinson to Massachusetts Attorney General Martha Coakley and Gov. Deval Patrick's Office of Consumer Affairs and Business Regulation. Eleazer declined to release a copy.

The involvement of the software had not been previously disclosed "because of the confidential nature of the investigation," Eleazer said. The breach remains under investigation by the U.S. Secret Service.
At least 1,800 cases of fraud have been linked to the data breach, with unauthorized charges showing up as far afield as Mexico, Italy and Bulgaria.
The breach has prompted concern in the industry because it appeared to be the first large-scale theft of credit and debit card numbers while the information was in transit. The usual mode of attack targets data sitting in databases, as in the record-setting theft of information from Massachusetts-based TJX Cos. involving least 45 million cards.
Even while the Hannaford hack was still going on last month, the company was found to be in compliance with security standards required by the Payment Card Industry, a coalition founded by credit card companies.